Overview:
This report outlines the process I used to discover an XSS vulnerability through triple URL encoding, which successfully bypassed the Web Application Firewall (WAF).
Steps to Discovery:
- Initial Payload Reflection: I started by testing a basic XSS payload:
"><svg onload=confirm()>This payload was reflected on the page but did not trigger any XSS alert. - First Encoding Attempt: I used an online URL encoding tool to encode the payload once and tested it again. The payload still did not trigger.
- Second Encoding Attempt: I encoded the payload a second time and retested. The payload remained non-functional.
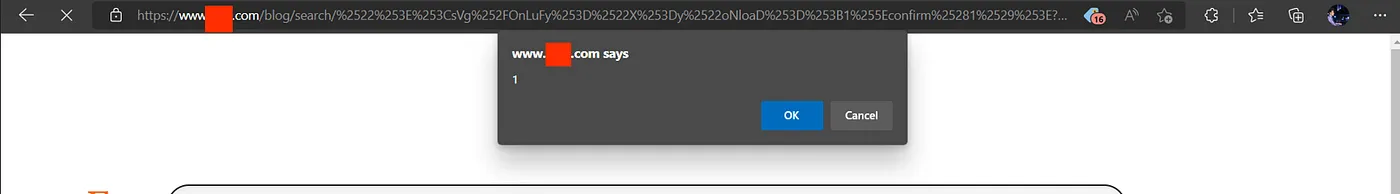
- Third Encoding Attempt: I encoded the payload a third time. This time, the payload successfully triggered an XSS alert, as shown in the image below.
Working Payload:
The final payload that worked after three URL encodings was:
%2522%253E%253CsVg%252FOnLuFy%253D%2522X%253Dy%2522oNloaD%253D%253B1%255Econfirm%25281%2529%253E
Reporting and Response:
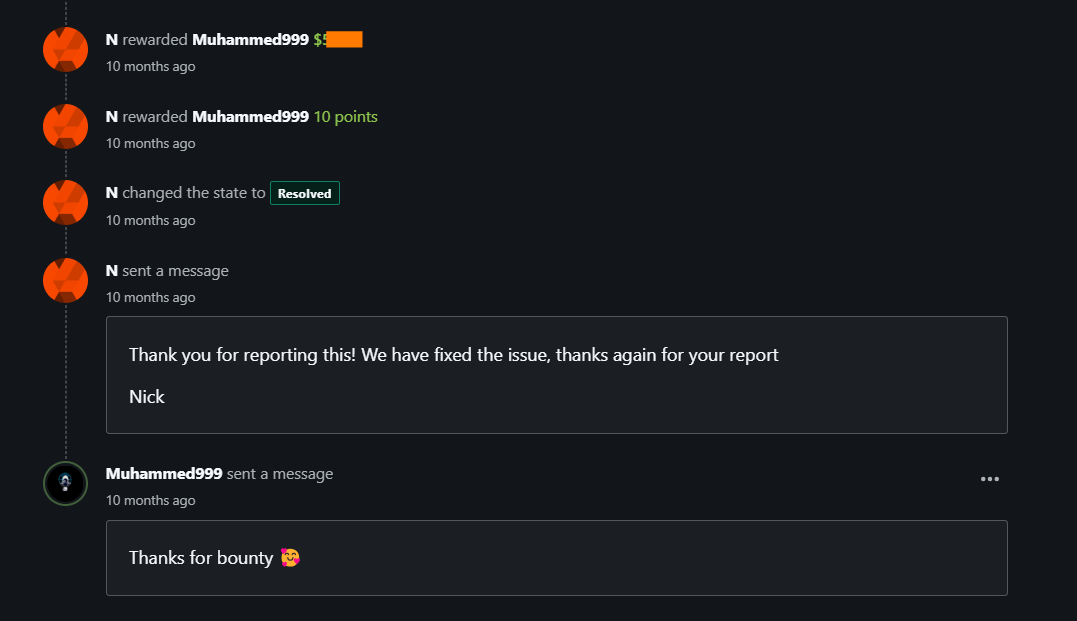
I reported this vulnerability to the security team. The submission status was changed to triaged within one day. The security team fixed the issue within two days as it affected the main domain. I received the bounty after 10 days.
Tips for Finding XSS:
- Try URL encoding.
- Try double URL encoding.
- Try triple URL encoding.
- Try Base64 encoding.
- Always review the source code to create the appropriate payload.
I hope this information is helpful to you.
Best regards, Secone4all_admin
No comments yet